
IAME — Microsoft 365
One identity, across the whole company.
IAME: migration from Google Workspace to Microsoft 365 for 46 users, around 2.7 TB of mail and files, with a single identity on Entra ID and devices managed with Intune. By Unlead.
- Client
- IAME
- Based in
- Verdellino (BG)
- Sector
- Motorsport
- Services
- Managed IT
The project
From Google Workspace to Microsoft 365: 46 users and a single identity for mail, documents and devices
The client
IAME has designed, manufactured and sold kart engines in Verdellino, in the province of Bergamo, since 1968, and through IAME Motorsport it organises championships around the world. It is part of the Korus group, which brings together Italian motorsport companies. For IAME we already look after the website and the championship platform.
The brief
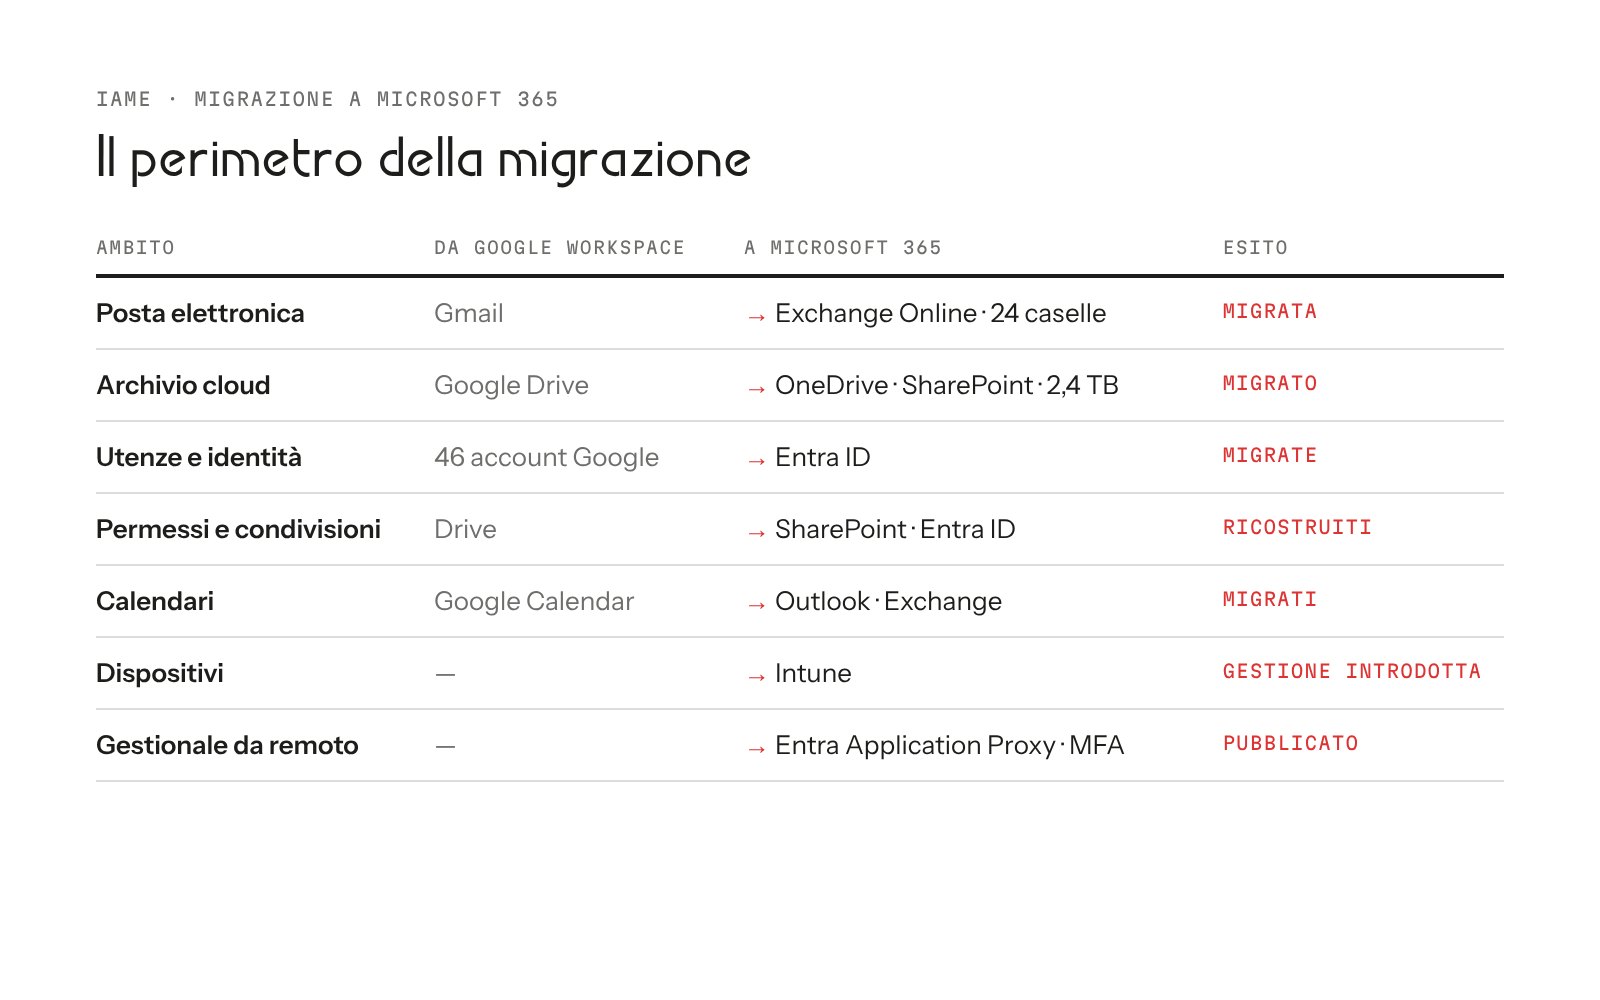
Moving the company from Google Workspace to Microsoft 365: mail, cloud storage, user accounts, permissions and calendars for 46 accounts. And not just changing mailboxes, but having an environment that governs identity, devices, documents and security from a single console.
The approach
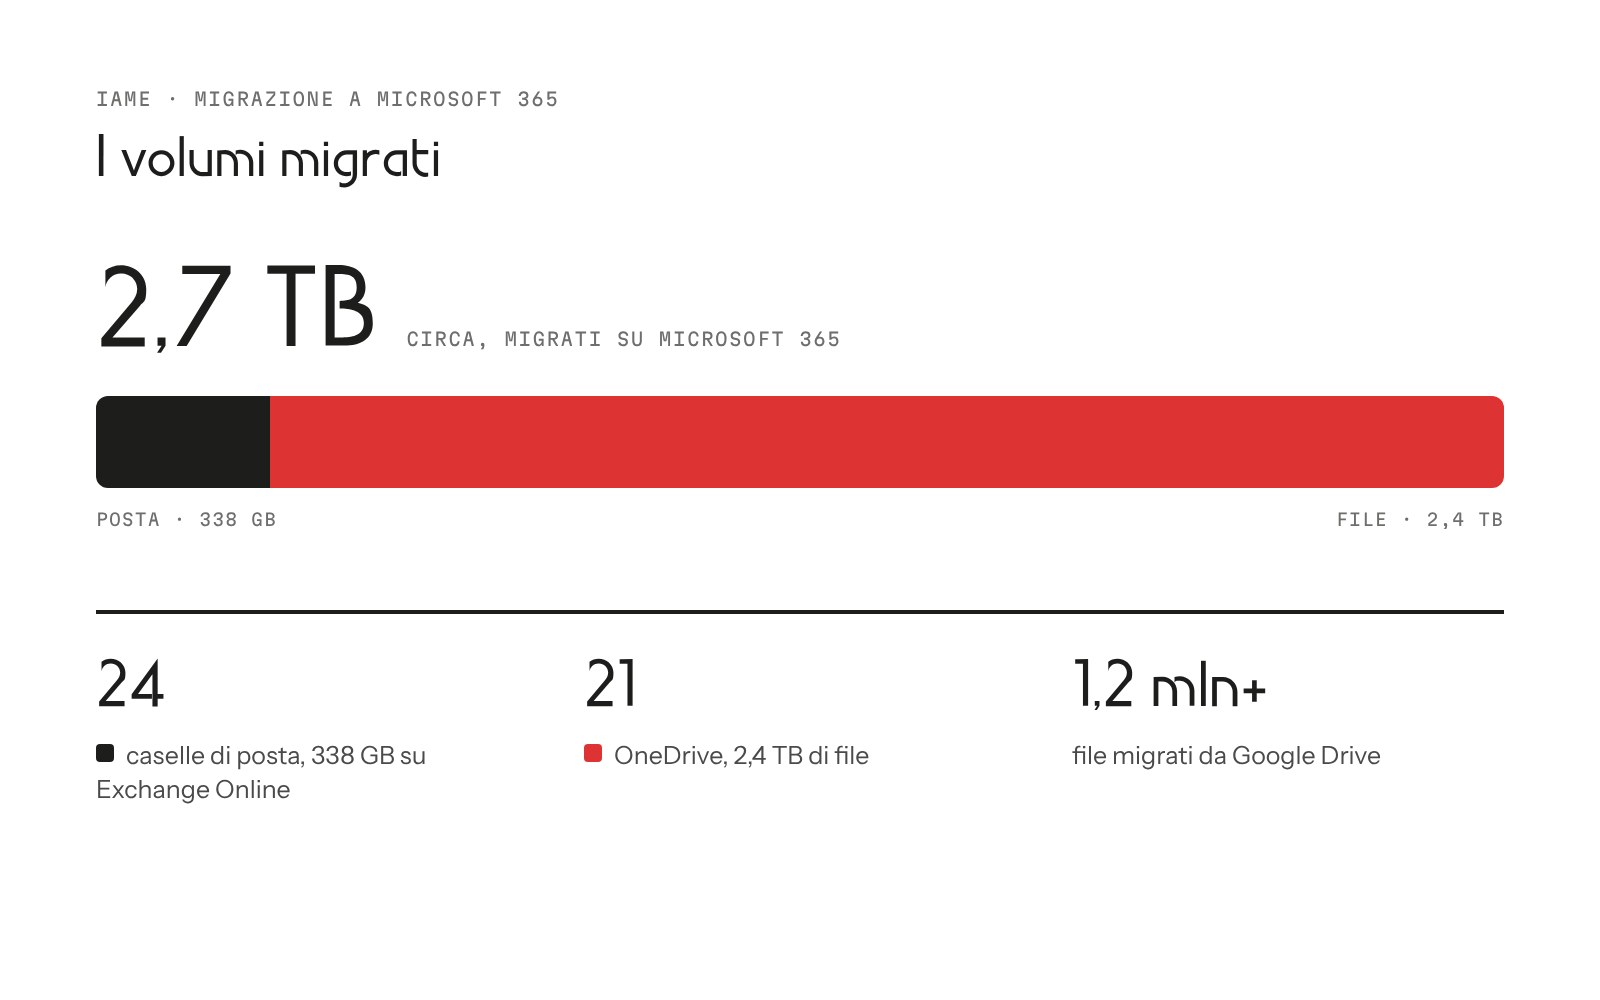
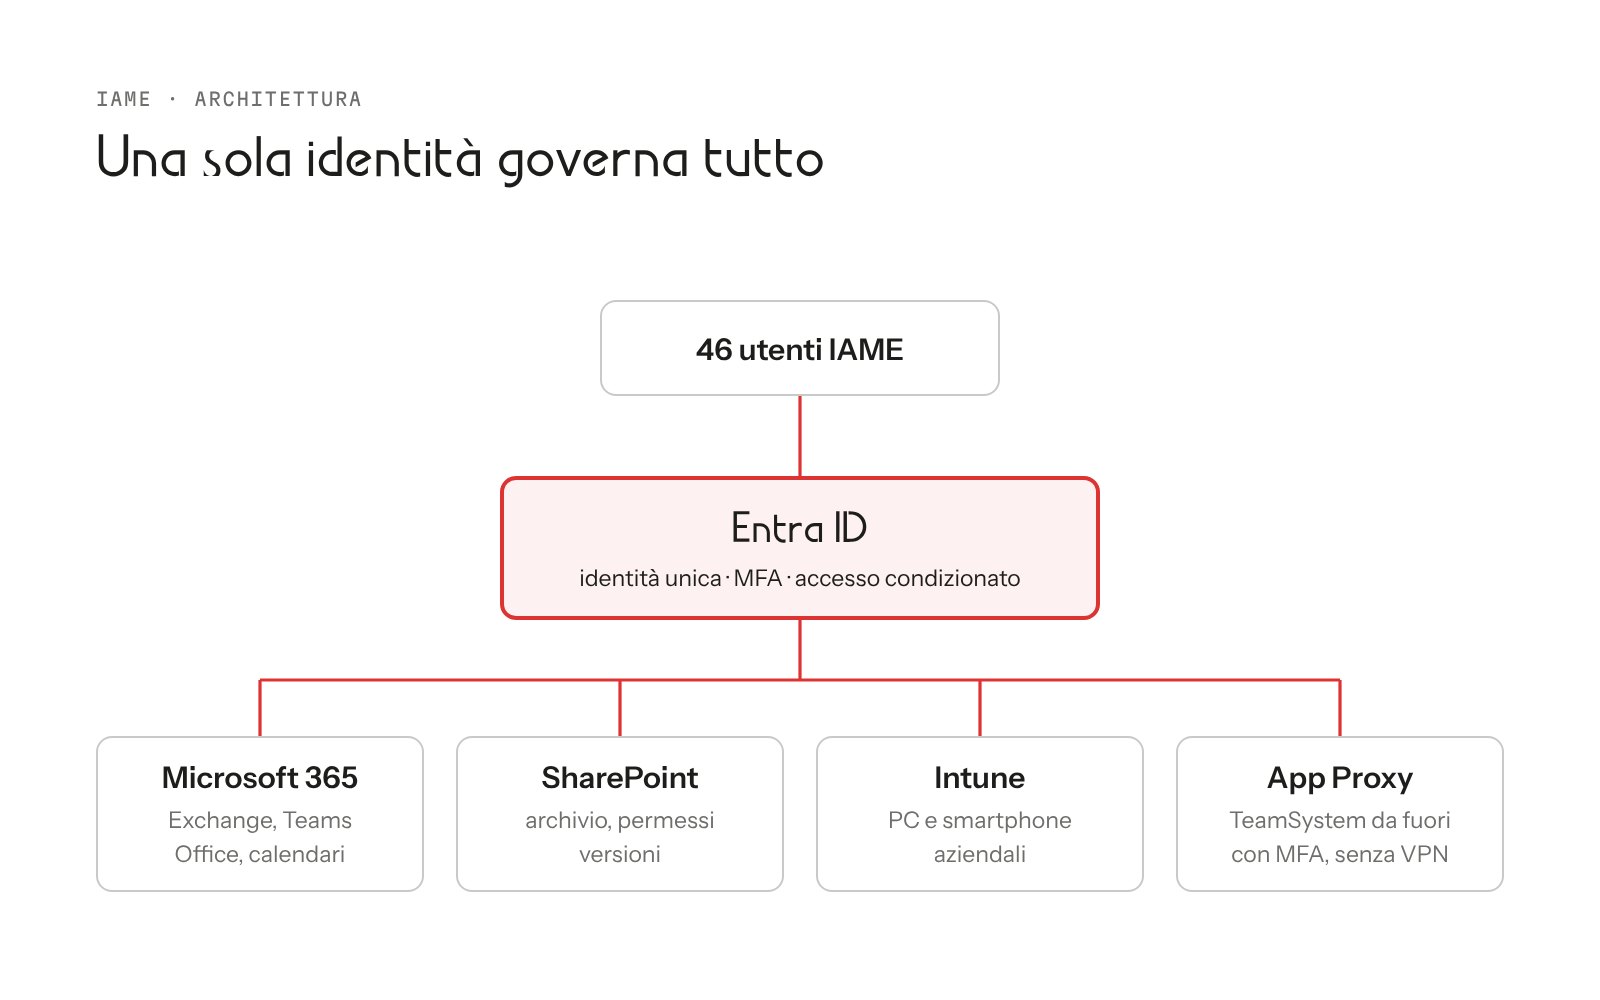
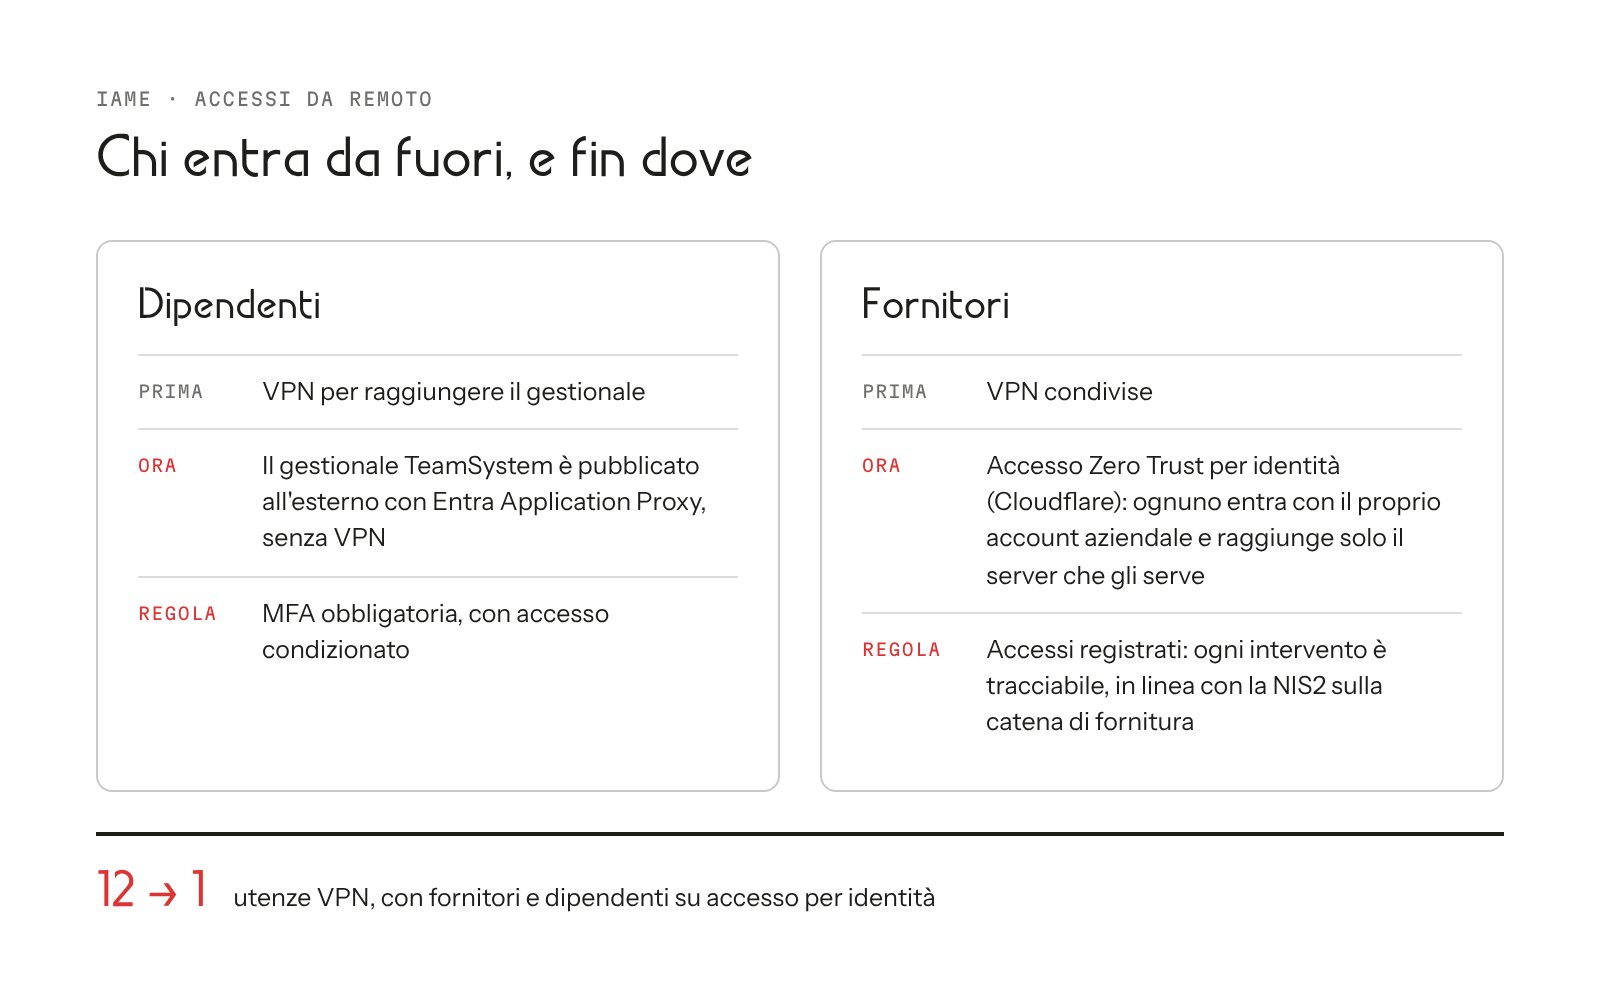
We migrated around 2.7 TB to Microsoft 365: 338 GB of mail across 24 mailboxes, from Gmail to Exchange Online, and 2.4 TB of files across 21 OneDrives, more than 1.2 million files in all. Calendars moved to Outlook, user accounts to Entra ID, and permissions were rebuilt in SharePoint. Entra ID is the point of control: every user accesses all services with a single identity, with multi-factor authentication and conditional access. We introduced Intune for company PCs and smartphones and joined the domain PCs to Microsoft 365 under a single identity. Access from outside goes through identity too. Employees reach the TeamSystem ERP, published externally with Entra Application Proxy, with mandatory MFA and no VPN. For suppliers, shared VPNs were replaced by identity-based Zero Trust access (Cloudflare): each supplier signs in with their own company account and reaches only the server they need, nothing else on the network. Access is logged, so every intervention is traceable, in line with what NIS2 requires on supply-chain security. This is a managed IT engagement: we continue to look after the environment.
- 2.7 TBmigrated to Microsoft 365, approximately
- 338 GBof mail across 24 mailboxes
- 2.4 TBof files across 21 OneDrives
- 1.2 m+files migrated
Project images
The results.
- 15users with a single identity across PCs and Microsoft 365, with the same password, joined without losing their mailbox, OneDrive or Teams
- 0users with admin rights on their own PCs, as NIS2 requires
- 30 daysthe lifetime of the local administrator password, managed by Intune
- 29obsolete objects retired: 22 inactive computers and 7 servers that no longer exist
- 12 → 1VPN accounts, with suppliers and employees on identity-based access
- 1single place to create a new employee, producing the account, mailbox and PC access
- BitLockerthe key of every encrypted PC is stored in the domain and can be recovered after a failure
- RDP offRemote Desktop off on all PCs and Network Level Authentication required on servers
- SBS offold server shut down: domain roles moved to the new controller and policy replication modernised
Our process, on every project
- 01AnalysisThe market, the business and who will use the result: we understand where we are starting from.
- 02FeasibilityNeeds, costs and benefits compared, to choose the right solution.
- 03DesignThe solution designed in detail and agreed before it is produced.
- 04ProductionGraphics, photos, video or code, checked against the agreed requirements.
- 05LaunchGo-live or delivery, with training for those who will use it.
- 06ManagementSupport, measurement of results and ongoing improvements.